#php

What this server has with the tag: posts by people here, and posts from elsewhere that reached it. There's more of it on mastodon.social, oslo.town, fosstodon.org, mastodon.online, floss.social.

@hacksgr@mastodon.social

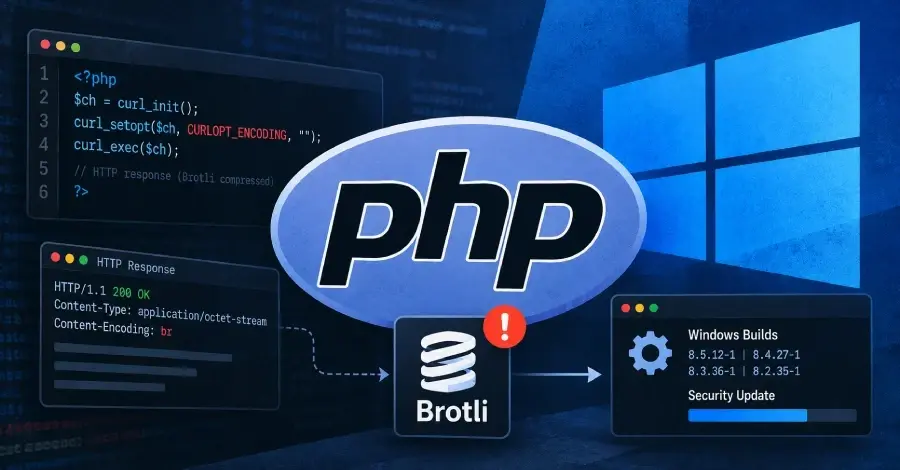
PHP has rebuilt official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a memory corruption vulnerability in the Brotli compression library.

The issue can be reached via the cURL extension when automatic HTTP response decompression is enabled.

Affected packages include versions 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, incorporating Brotli 1.2.1.

Windows users are advised to update from the official downloads page.

en.hacks.gr/nea-paketa-php-gia

Νέα πακέτα PHP για τα Windows διορθώνουν σοβαρό πρόβλημα ασφαλείας
@php@fosstodon.org

📣 Announcing the immediate availability of:

- PHP 8.2.35
- PHP 8.3.36
- PHP 8.4.27
- PHP 8.5.12

‼️ These address the following critical security issues:

- Remote Code Execution via Out of Memory corruption (CVE-2026-109618)
- Remote Code Execution via Stale Global State (CVE-2026-109619)

📝 php.net/ChangeLog-8.php
🎁 php.net/downloads?source=Y
:windows8: Windows: php.net/downloads.php?os=windo

Read more: php.net/archive/2026.php#2026-

@BjornW@mastodon.social

The PHP issue shows once again how much our society relies on mostly volunteer work.

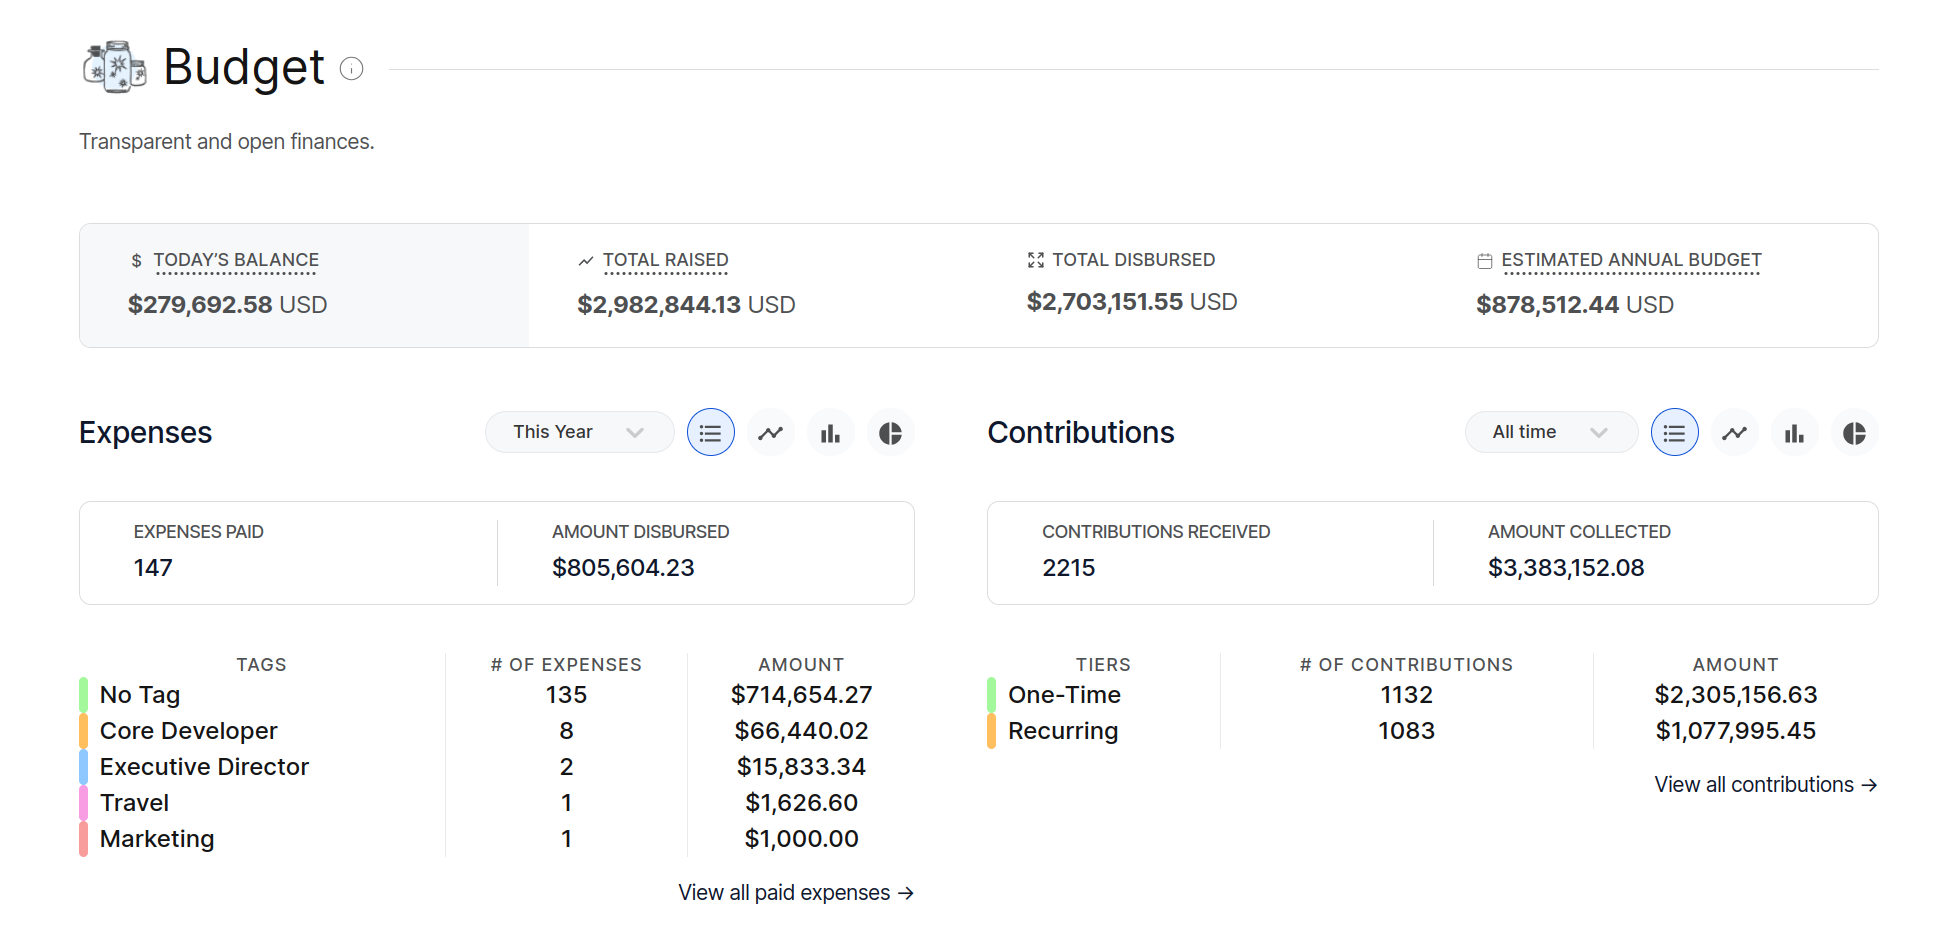
Look at PHP Foundation @thephpf finances:
opencollective.com/phpfoundati

- Reimbursed $67K on development work this year
- Received: $642,755 last year

Compare these numbers with the amounts companies have made with products & services built upon . Our digital foundations are built on the backs of volunteers. Governments & companies need to invest in our common digital infrastructures.

Screenshot of the PHP Foundation's finances on Open Collective
@hywan@floss.social

High-severity vulnerability in PHP. No patch yet. It’s coming (see @php). It’s recommended to simply shutdown your PHP applications until the patches land (as it involves remote code execution).

fosstodon.org/@php/11747497797