daniel:// stenberg://@bagder@mastodon.social
#curl 30th anniversary cake meeting link: https://meet.jit.si/cake-cake-cake-cake
What this server has with the tag: posts by people here, and posts from elsewhere that reached it. There's more of it on mastodon.social, chaos.social, mastodon.ie, infosec.exchange.
#curl 30th anniversary cake meeting link: https://meet.jit.si/cake-cake-cake-cake
#curl cake video meeting at 15:00 CET (14:00 UTC) today. Link to join follows later.
Many thanks to Rafael Sagula† and @bagder on having the forsight 30 years ago to start creating the #curl we have today.
There is this video format „what would our world be without…“ where one thing after another blinks out of existence.
So, I start and you add via comments, ok?
Without curl there would be no:
- Netflix
In reply to @bagder@mastodon.social
out of Anthropic's latest 45 findings in #curl, we are at 7 confirmed LOW. 37 "just a bug" and one completely false.
for those who follow: yeah, we're gradually raising the bar for what we accept as LOW severity #curl vulnerabilities.
In the midst of the avalanche, I managed to make the cookie receive performance test in #curl run 10% faster, with each cookie now kept using a *single* malloc instead of five like before
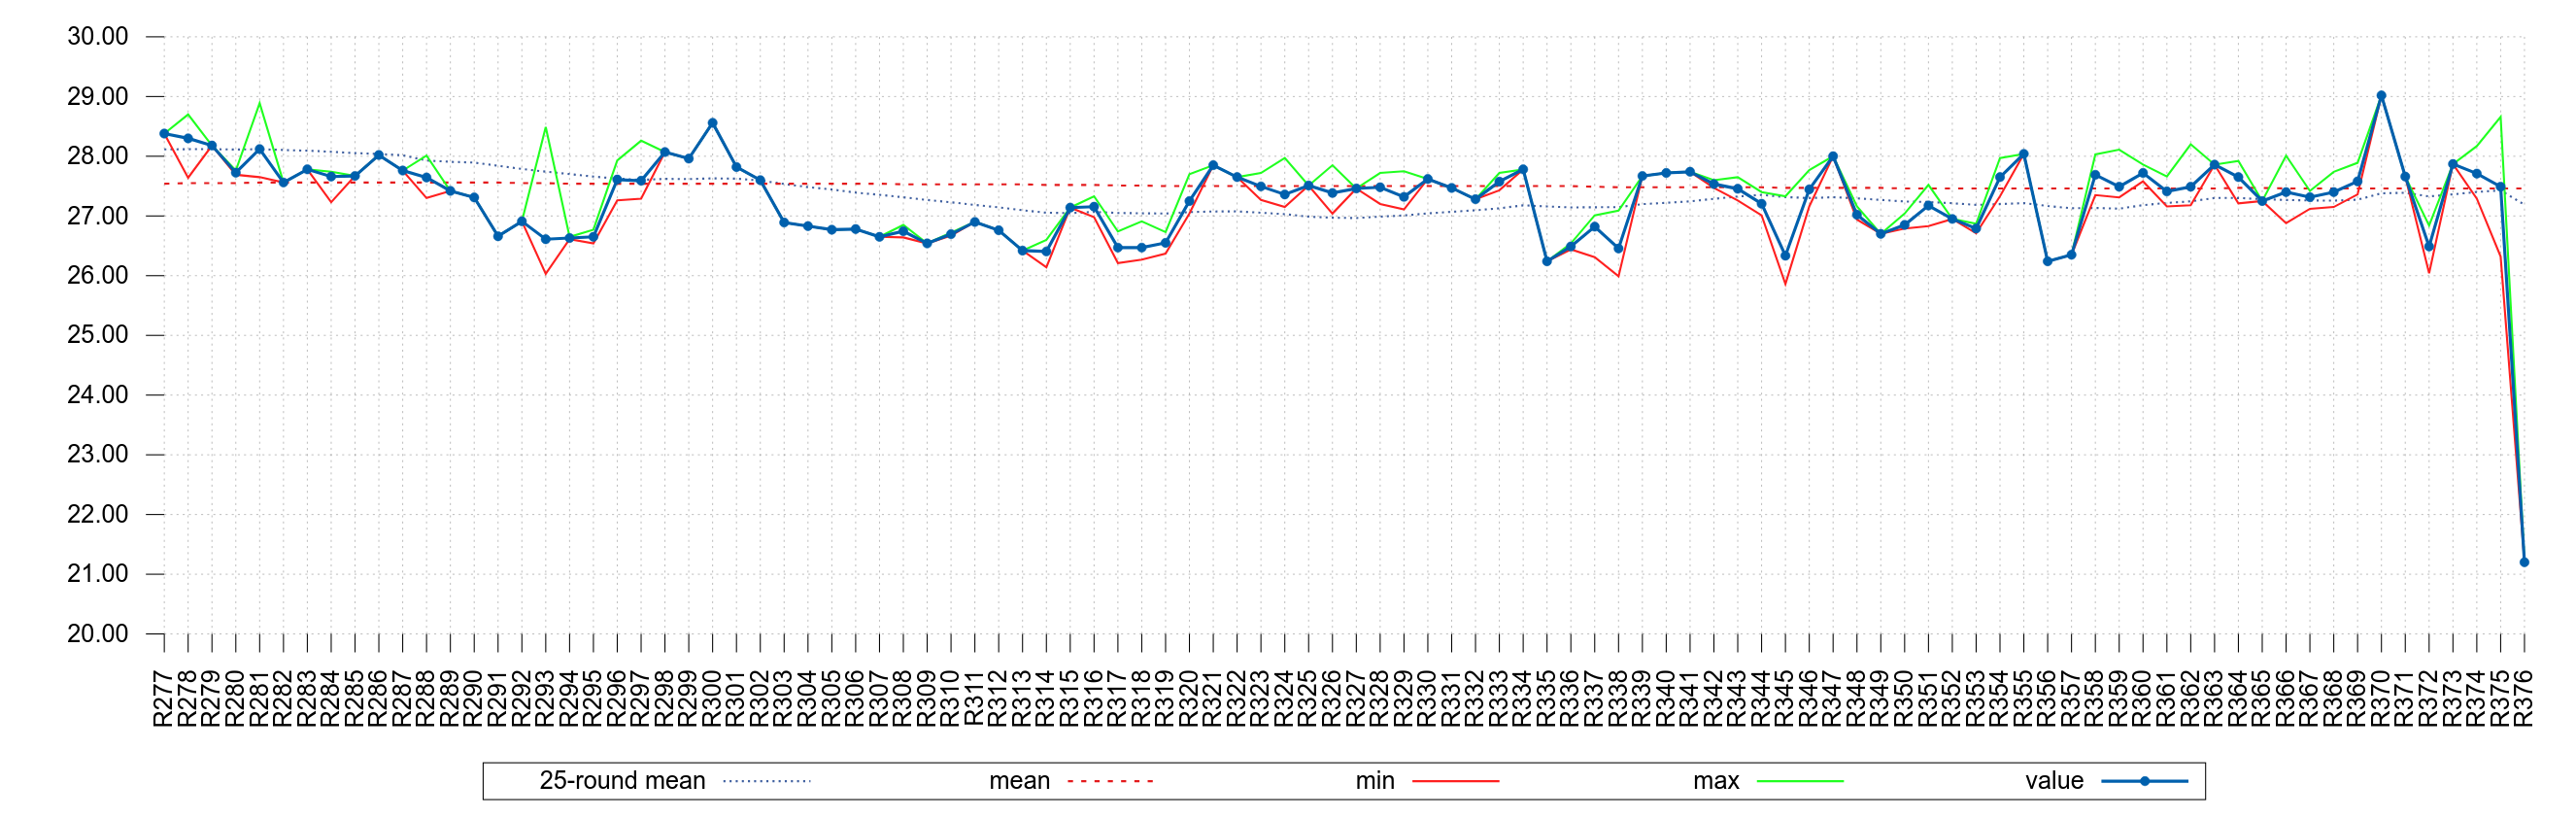
In the 27 days since the previous #curl release, we've merged 218 bugfixes written by 49 authors and we have 19 CVEs in the queue for publication...
Welcome kaushal-pratap as #curl commit author 1578: https://github.com/curl/curl/issues/23857
Welcome Aaron Johnstone as #curl commit author 1577: https://github.com/curl/curl/issues/23789
Welcome Rudransh Shekhar as #curl commit author 1576: https://github.com/curl/curl/issues/23863
here are the 45 findings Anthropic reported to #curl last week: https://github.com/curl/curl/issues?q=is%3Aissue+ANT-2026
don't forget to order yourself a cake for Wednesday to properly partake in the #curl 30 years celebrations
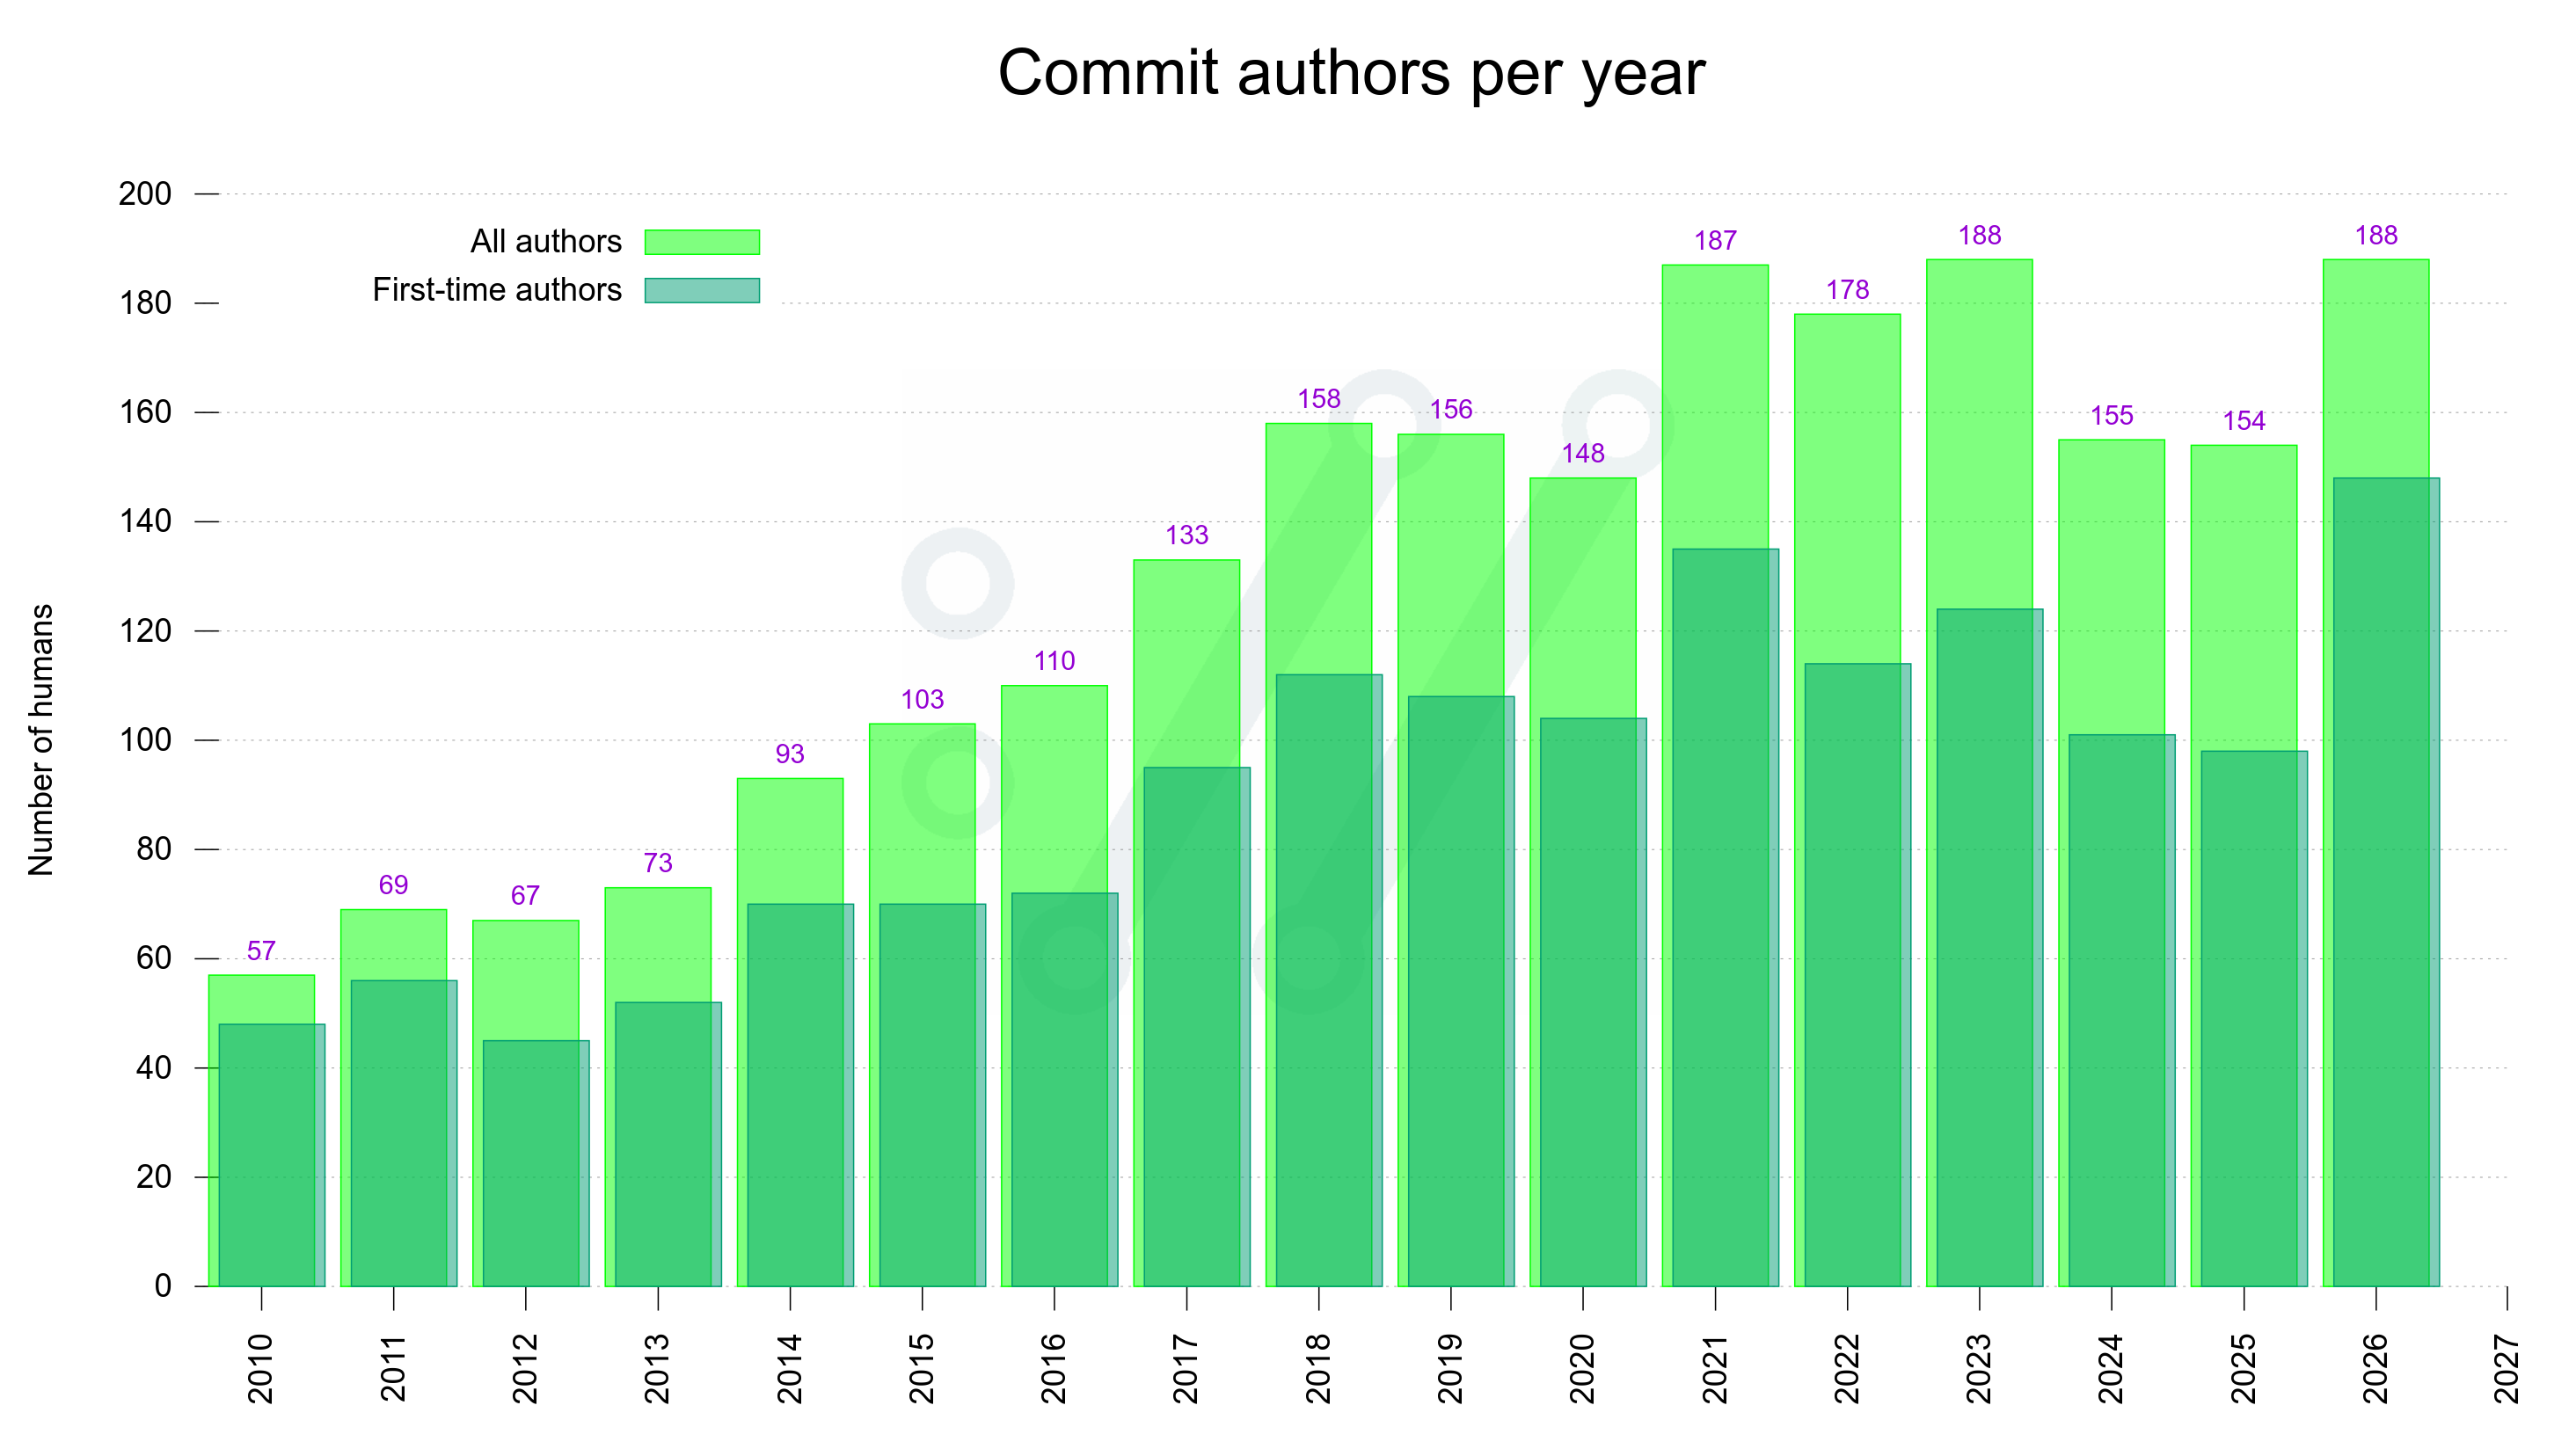
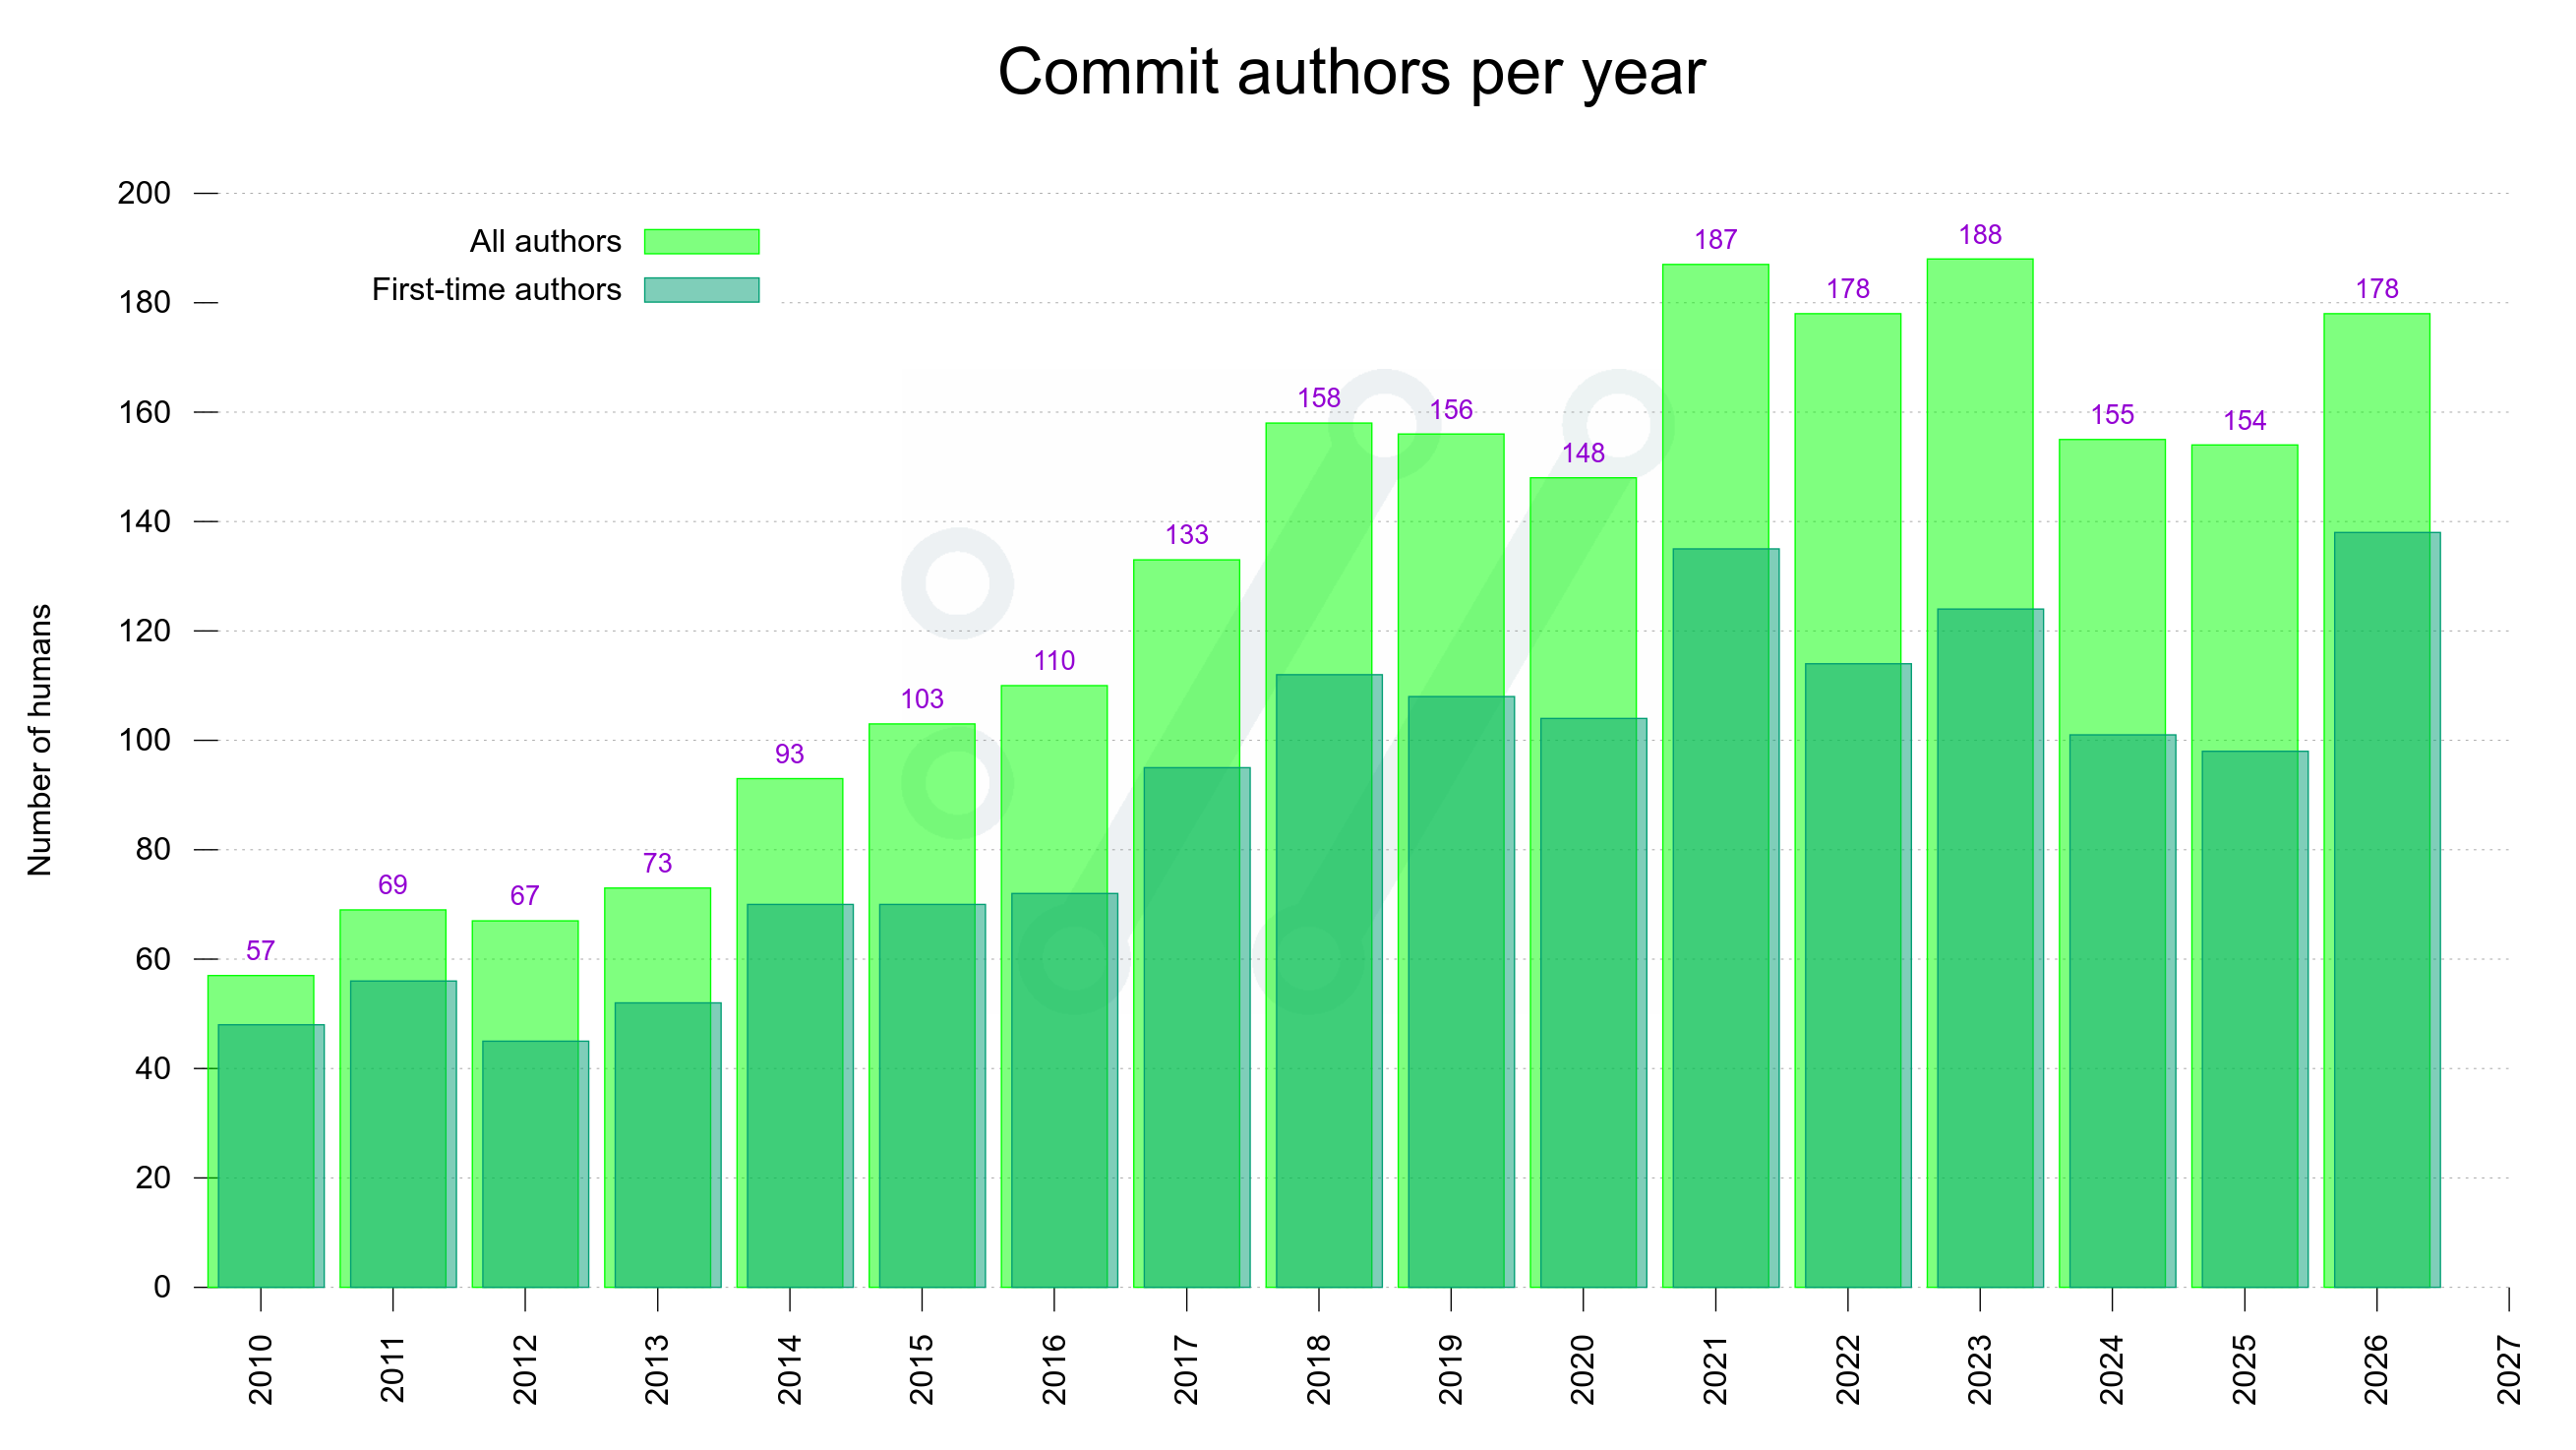
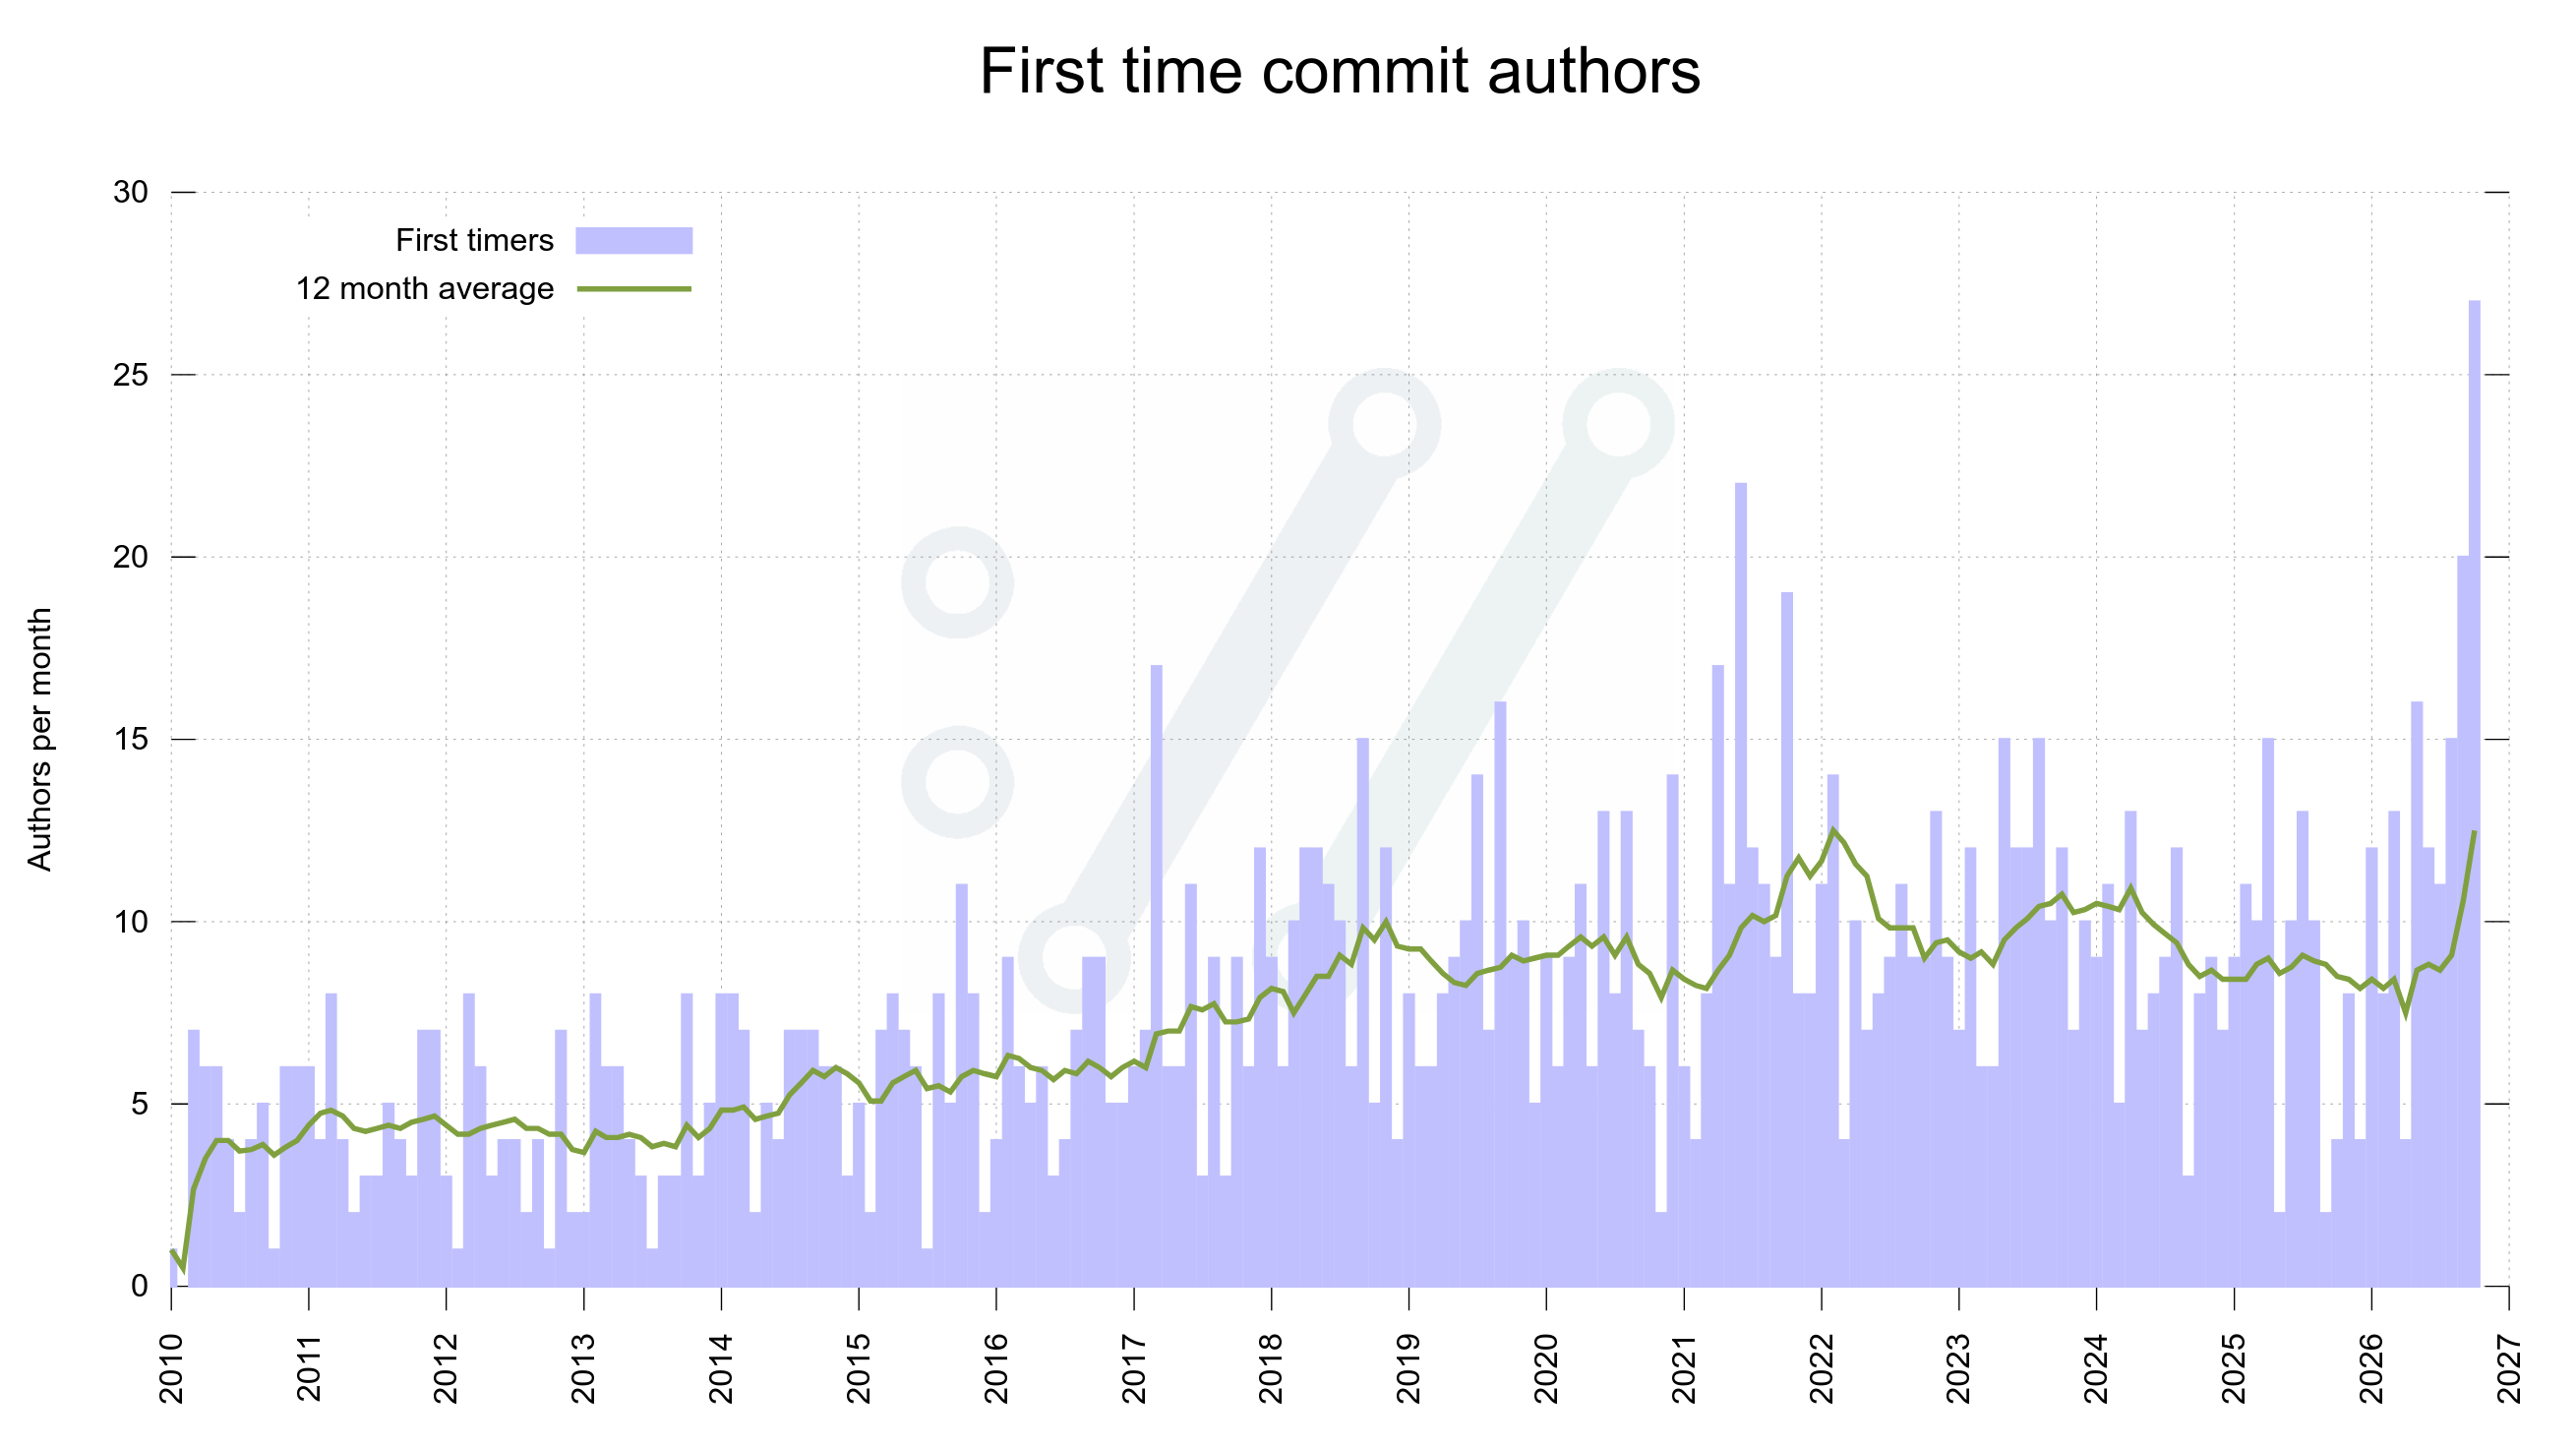
commit authors per year in #curl... and look at the share of first timers there.
thank you awesome #curl contributors for stepping in and helping out in these trying times
Welcome lazerg as #curl commit author 1574: https://github.com/curl/curl/issues/23815
at 17 confirmed #curl vulns since the previous release, 24 days ago
so far, we have four LOW #curl vulns confirmed from Anthropic's last batch, but we have over two dozens of findings left to dig through: https://github.com/curl/curl-www/issues?q=is%3Aissue+state%3Aopen+label%3Avuln%3ALOW
Aggressively closing #curl vulnerability reports on a Saturday. Again.
Welcome hja as #curl commit author 1573: https://github.com/curl/curl/issues/23784
I've copied over the 10 first vuln reports from Anthropic to #curl's GitHub issue tracker, keeping the remaining 35 off a little while to not drown us at once. Now you can get a good insight into what our lives look like these days:
https://github.com/curl/curl/issues?q=is%3Aissue+state%3Aopen+label%3Avuln%3AASSESS
Quite many #curl versions out there:
yesterday the #curl project got an email from a person announcing their grand new project to security audit a range of Open Source projects. Got a fancy project name and all. Asked for permission.
Two hours later the same person emailed us again, announcing that he shuts down this effort blaming "widespread failure affecting Codex".
We never got to respond. Moving on.
and why not 25% faster date parsing in #curl?
#curl 30 years gource visualization with Daniel's comments
Scrutinize the #curl vulnerability assessments:
https://daniel.haxx.se/blog/2026/11/03/scrutinize-our-assessments/
Welcome RubenPari as #curl commit author 1572: https://github.com/curl/curl/issues/23594
With the new #curl open policy for vulns, feel free to chime in and assess this report. Vuln or not? https://github.com/curl/curl/issues/23699
Welcome Stefan Reinauer as #curl commit author 1571: https://github.com/curl/curl/issues/23695
Handed out a few hundred #curl stickers at FOSSCOMM. Mission accomplished.
Welcome heppycat as #curl commit author 1569: https://github.com/curl/curl/issues/23670
I understand you've all been longing for them, and now the #curl builds for #QNX are in sync with the latest again: https://curl.se/qnx/
Welcome Mohammadreza Khellat as #curl commit author 1568: https://github.com/curl/curl/issues/23667
Welcome Vishnu Srivatsava as #curl commit author 1567: https://github.com/curl/curl/issues/23657
Welcome akasakariko as #curl commit author 1566: https://github.com/curl/curl/issues/23653
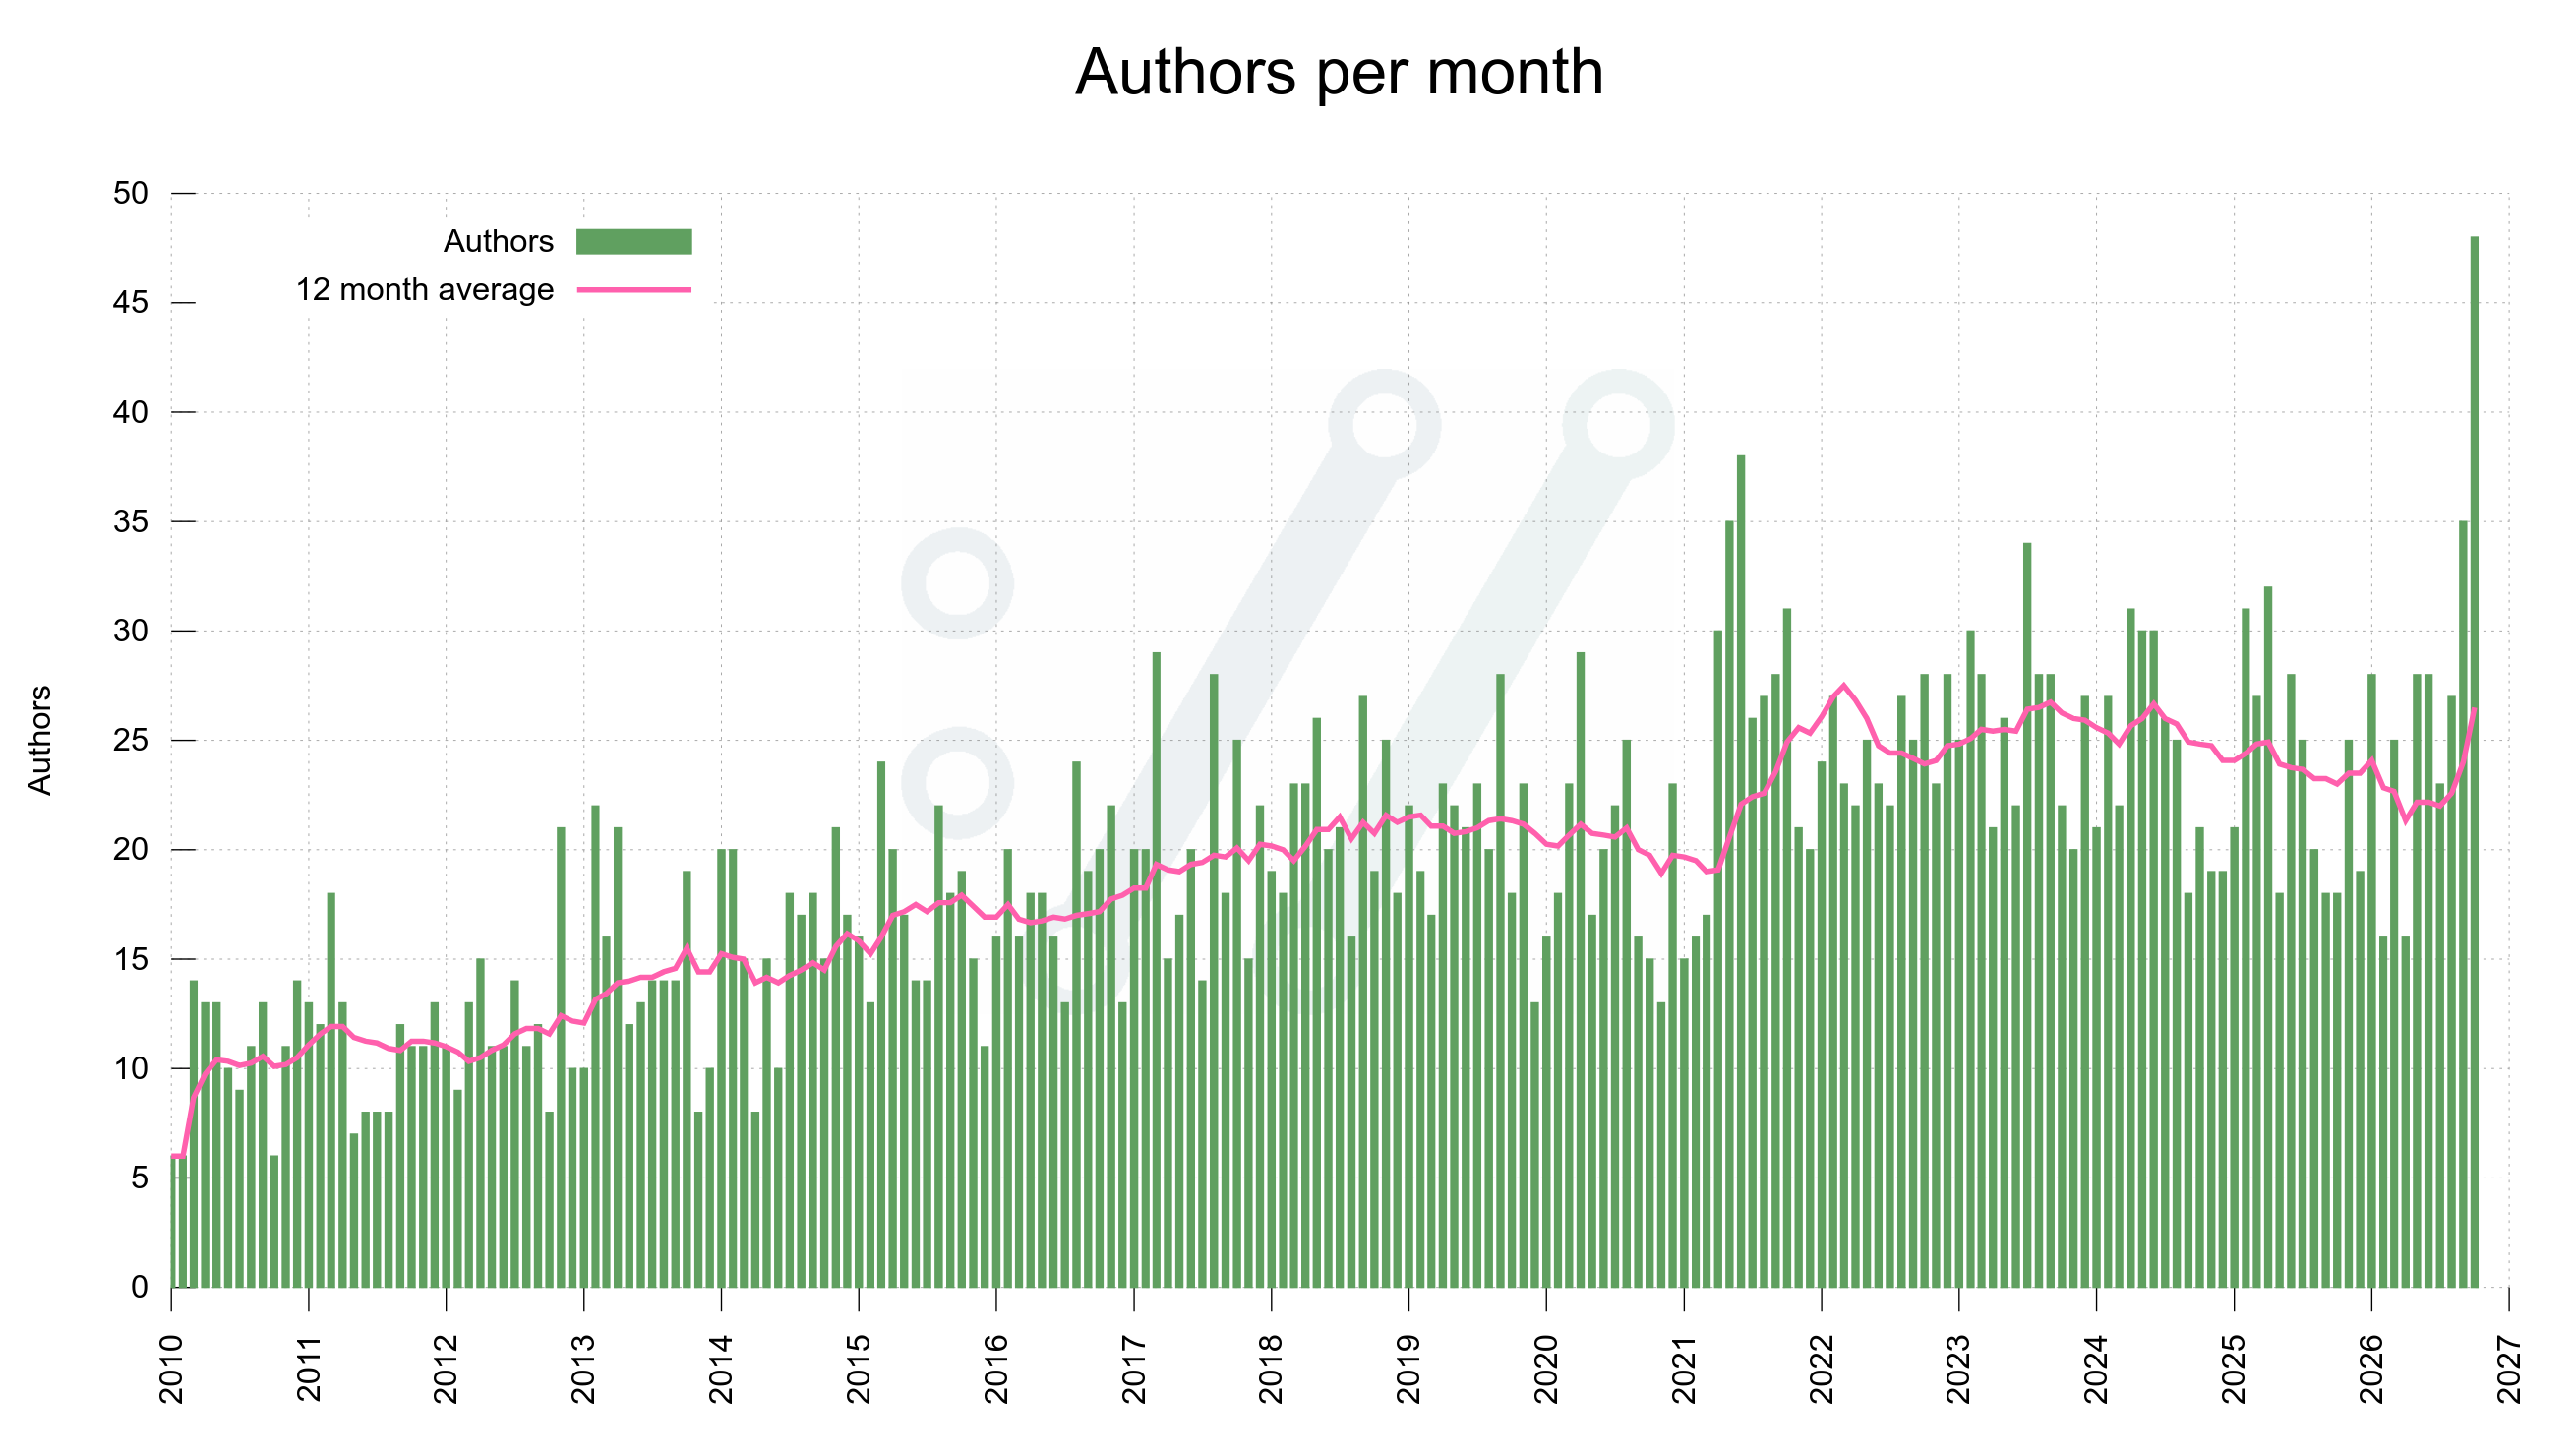
state of #curl dev in three graphs
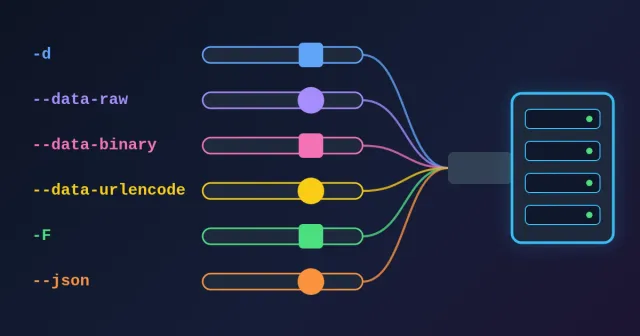
-d, --data-raw, --data-binary, --data-urlencode, -F, --json: what each curl option really sends, which Content-Type it sets, and how it maps to fetch and Python requests.
https://findutils.com/blog/curl-data-options-explained-d-data-raw-data-urlencode-form-json/
#curl #webdev
In reply to @bagder@mastodon.social
Welcome Bob Swanson as #curl commit author 1565: https://github.com/curl/curl/issues/23236
The OpenSSF scorecard scores #curl 8.9 out of 10. https://scorecard.dev/viewer/?uri=github.com/curl/curl
Yeah...
I wrote a blog that explains why why the new #curl security policy to not embargo low and medium vulnerabilities is a great idea and other open source projects should adopt this policy
https://opensourcesecurity.io/2026/10-embargo/
#OpenSourceSecurity #vulnerability #embargo #security #opensource
PHP has rebuilt official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a memory corruption vulnerability in the Brotli compression library.
The issue can be reached via the cURL extension when automatic HTTP response decompression is enabled.
Affected packages include versions 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, incorporating Brotli 1.2.1.
Windows users are advised to update from the official downloads page.
https://en.hacks.gr/nea-paketa-php-gia-ta-windows-diorthonoyn-sovaro-provlima-asfaleias/
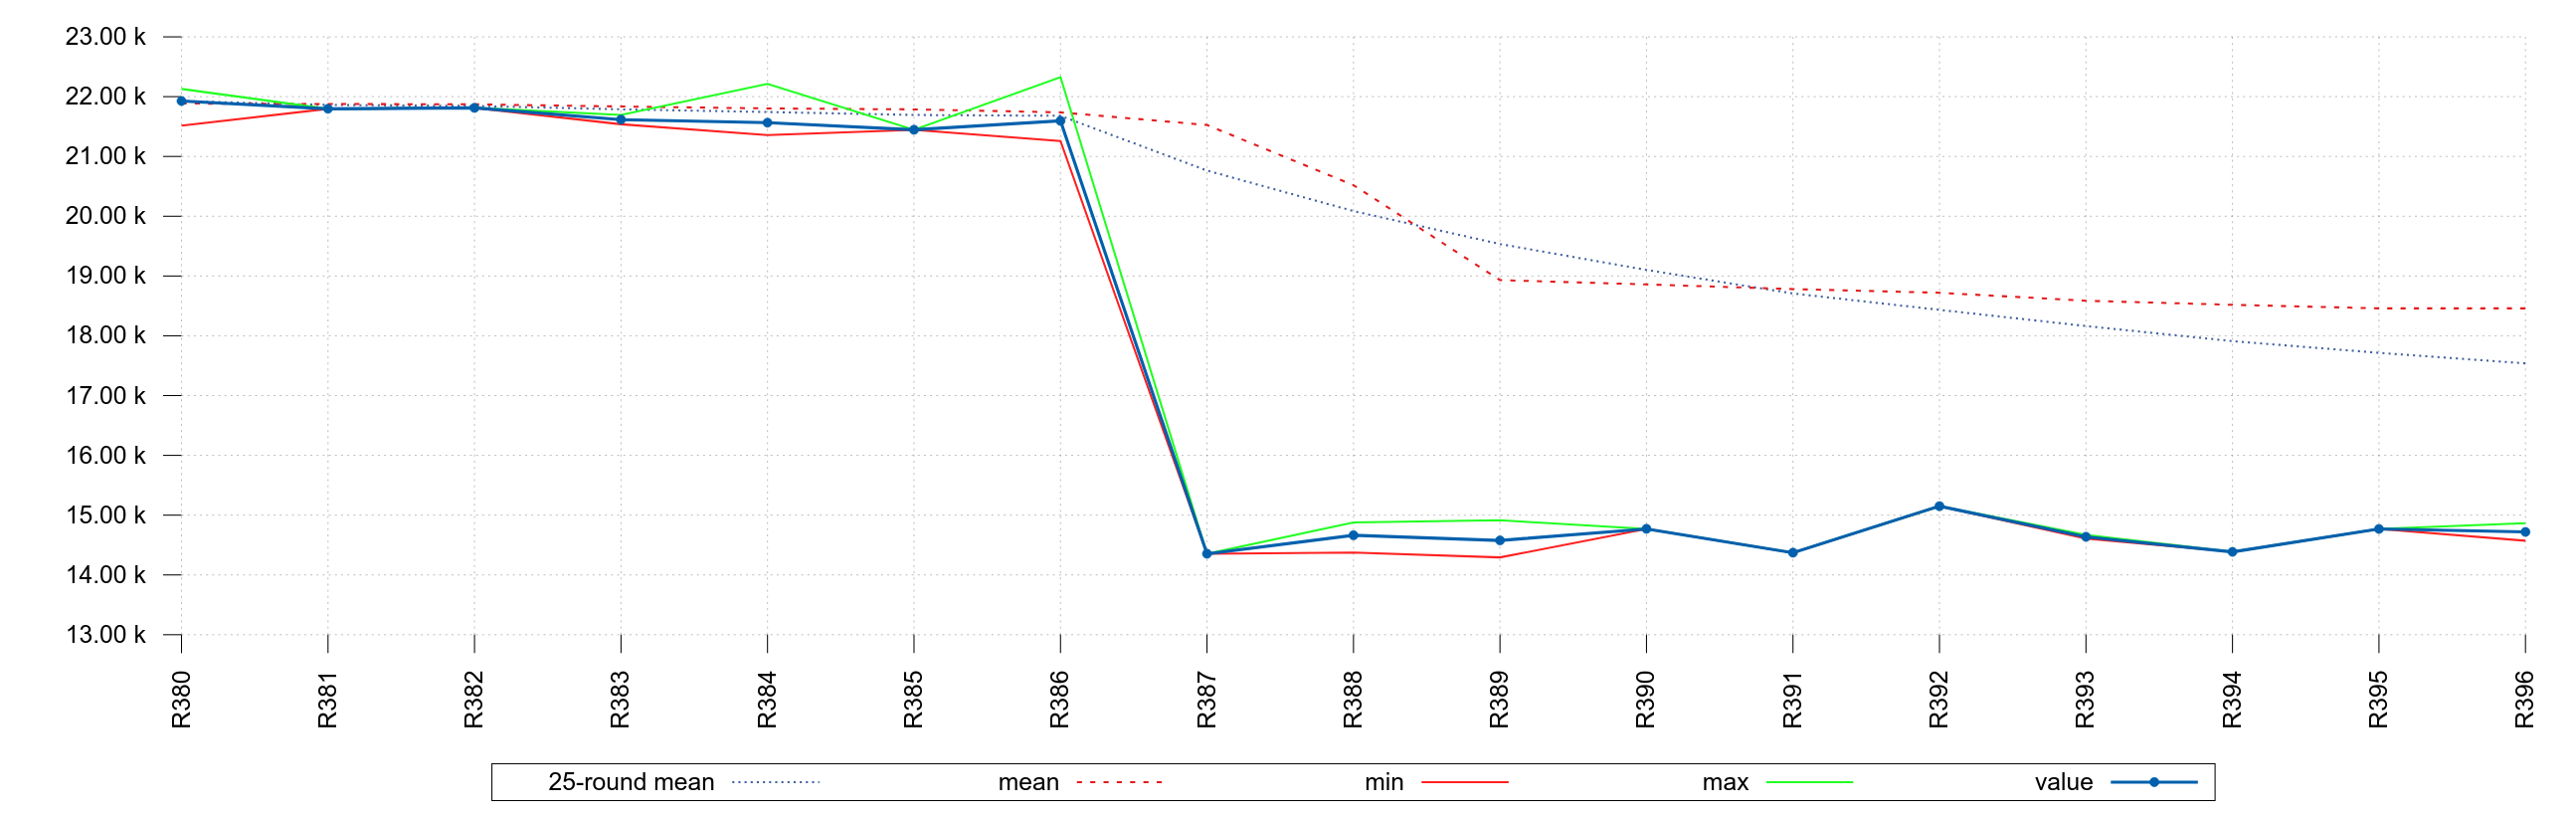
In other news: #curl's HTTP response parser got 50% faster parsing a response with 200 headers!
Welcome Sai Harsha as #curl commit author 1564: https://github.com/curl/curl/pull/23582
In reply to a post
@emersion there is no obligation for you to handle CVEs at all, you can decide yourself. But you should be aware that others might still get CVEs for your software, because that's how CVEs work. You can certainly decide to manage all the vulns in the public if you want. That's your choice. In #curl we just switched to handle all LOW and MEDIUM issues publicly.
Welcome trestoncuzzort as #curl commit author 1563: https://github.com/curl/curl/pull/23600
Welcome to the new #curl vulnerability disclosure policy: https://curl.se/dev/vuln-disclosure.html
13 pending security advisories currently being worked on in the public: https://github.com/curl/curl-www/pulls
Welcome Armaan Sandhu as #curl commit author 1562: https://github.com/curl/curl/pull/23581
Welcome Derek Martin as #curl commit author 1561: https://github.com/curl/curl/pull/23577
We are sticking to December 9 as release date for the pending #curl release: https://curl.se/mail/lib-2026-10/0014.html
The curl sticker distribution system has been triggered to please the people going to the RIPE meeting next week. There shall be #curl stickers present.
allheim has been updated.