#brotli

What this server has with the tag: posts by people here, and posts from elsewhere that reached it. There's more of it on mastodon.social, infosec.exchange.

@hacksgr@mastodon.social

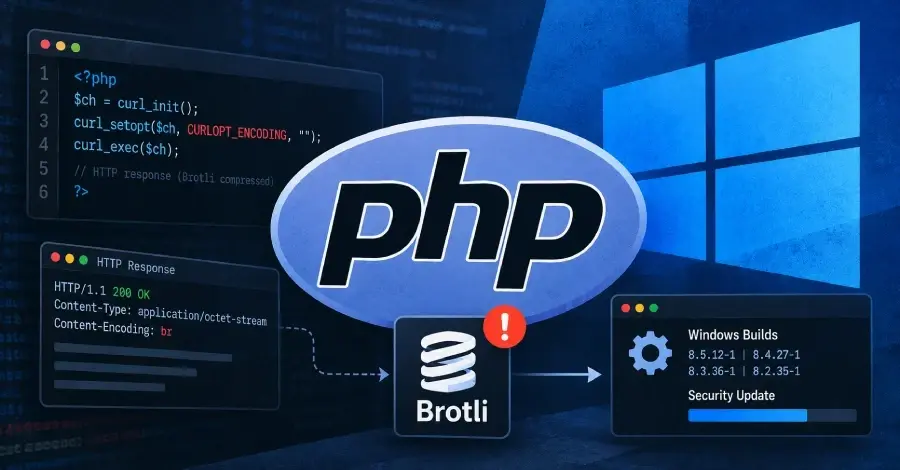
PHP has rebuilt official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a memory corruption vulnerability in the Brotli compression library.

The issue can be reached via the cURL extension when automatic HTTP response decompression is enabled.

Affected packages include versions 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, incorporating Brotli 1.2.1.

Windows users are advised to update from the official downloads page.

en.hacks.gr/nea-paketa-php-gia

Νέα πακέτα PHP για τα Windows διορθώνουν σοβαρό πρόβλημα ασφαλείας
@harrysintonen@infosec.exchange

command https remote is affected by the buffer overflow vulnerability CVE-2026-111497 since it enables compression support:

github.com/git/git/blob/7e34d8

Make sure to update brotli as soon as possible.

github.com/advisories/GHSA-9v8

@harrysintonen@infosec.exchange

For some reason the CVE-2026-111497 buffer overflow vulnerability in the decoder is mostly associated with , but this is far more wider issue. Brotli compression is supported by many client side applications processing HTTP responses. While some of them have sandboxes and quick update cycle (read: web browsers), many don't. In particular many devices and applications using / libcurl are affected and must be updated ASAP.

github.com/advisories/GHSA-9v8
nvd.nist.gov/vuln/detail/cve-2