#curl

What this server has with the tag: posts by people here, and posts from elsewhere that reached it. There's more of it on infosec.exchange, mastodon.social, mastodon.nu, chaos.social.

@harrysintonen@infosec.exchange

For some reason the CVE-2026-111497 buffer overflow vulnerability in the decoder is mostly associated with , but this is far more wider issue. Brotli compression is supported by many client side applications processing HTTP responses. While some of them have sandboxes and quick update cycle (read: web browsers), many don't. In particular many devices and applications using / libcurl are affected and must be updated ASAP.

github.com/advisories/GHSA-9v8
nvd.nist.gov/vuln/detail/cve-2

@bagder@mastodon.social

on Monday I will create 13 new pull-requests with the pending Security Advisories for coming CVEs with severity LOW or MEDIUM. Then our new policy takes effect and a lot less vulnerability work in curl will be done in private, and almost all of it will go public. You are all invited to help out.

@vsz@mastodon.social

8.23.0_3 update released at curl.se/windows/. It no longer ships with a CA bundle. Since 8.19.0 (2026-03-11) curl and libcurl are using the native Windows CA roots by default. I kept including the CA bundle to serve as a manual fallback, in case the native CA fails. This option remains, but the bundle needs to be downloaded separately. If you use an official curl release older than this, consider upgrading to 8.19.0+, or refresh the CA bundle to avoid the compromised eMudhra certs.

@bagder@mastodon.social

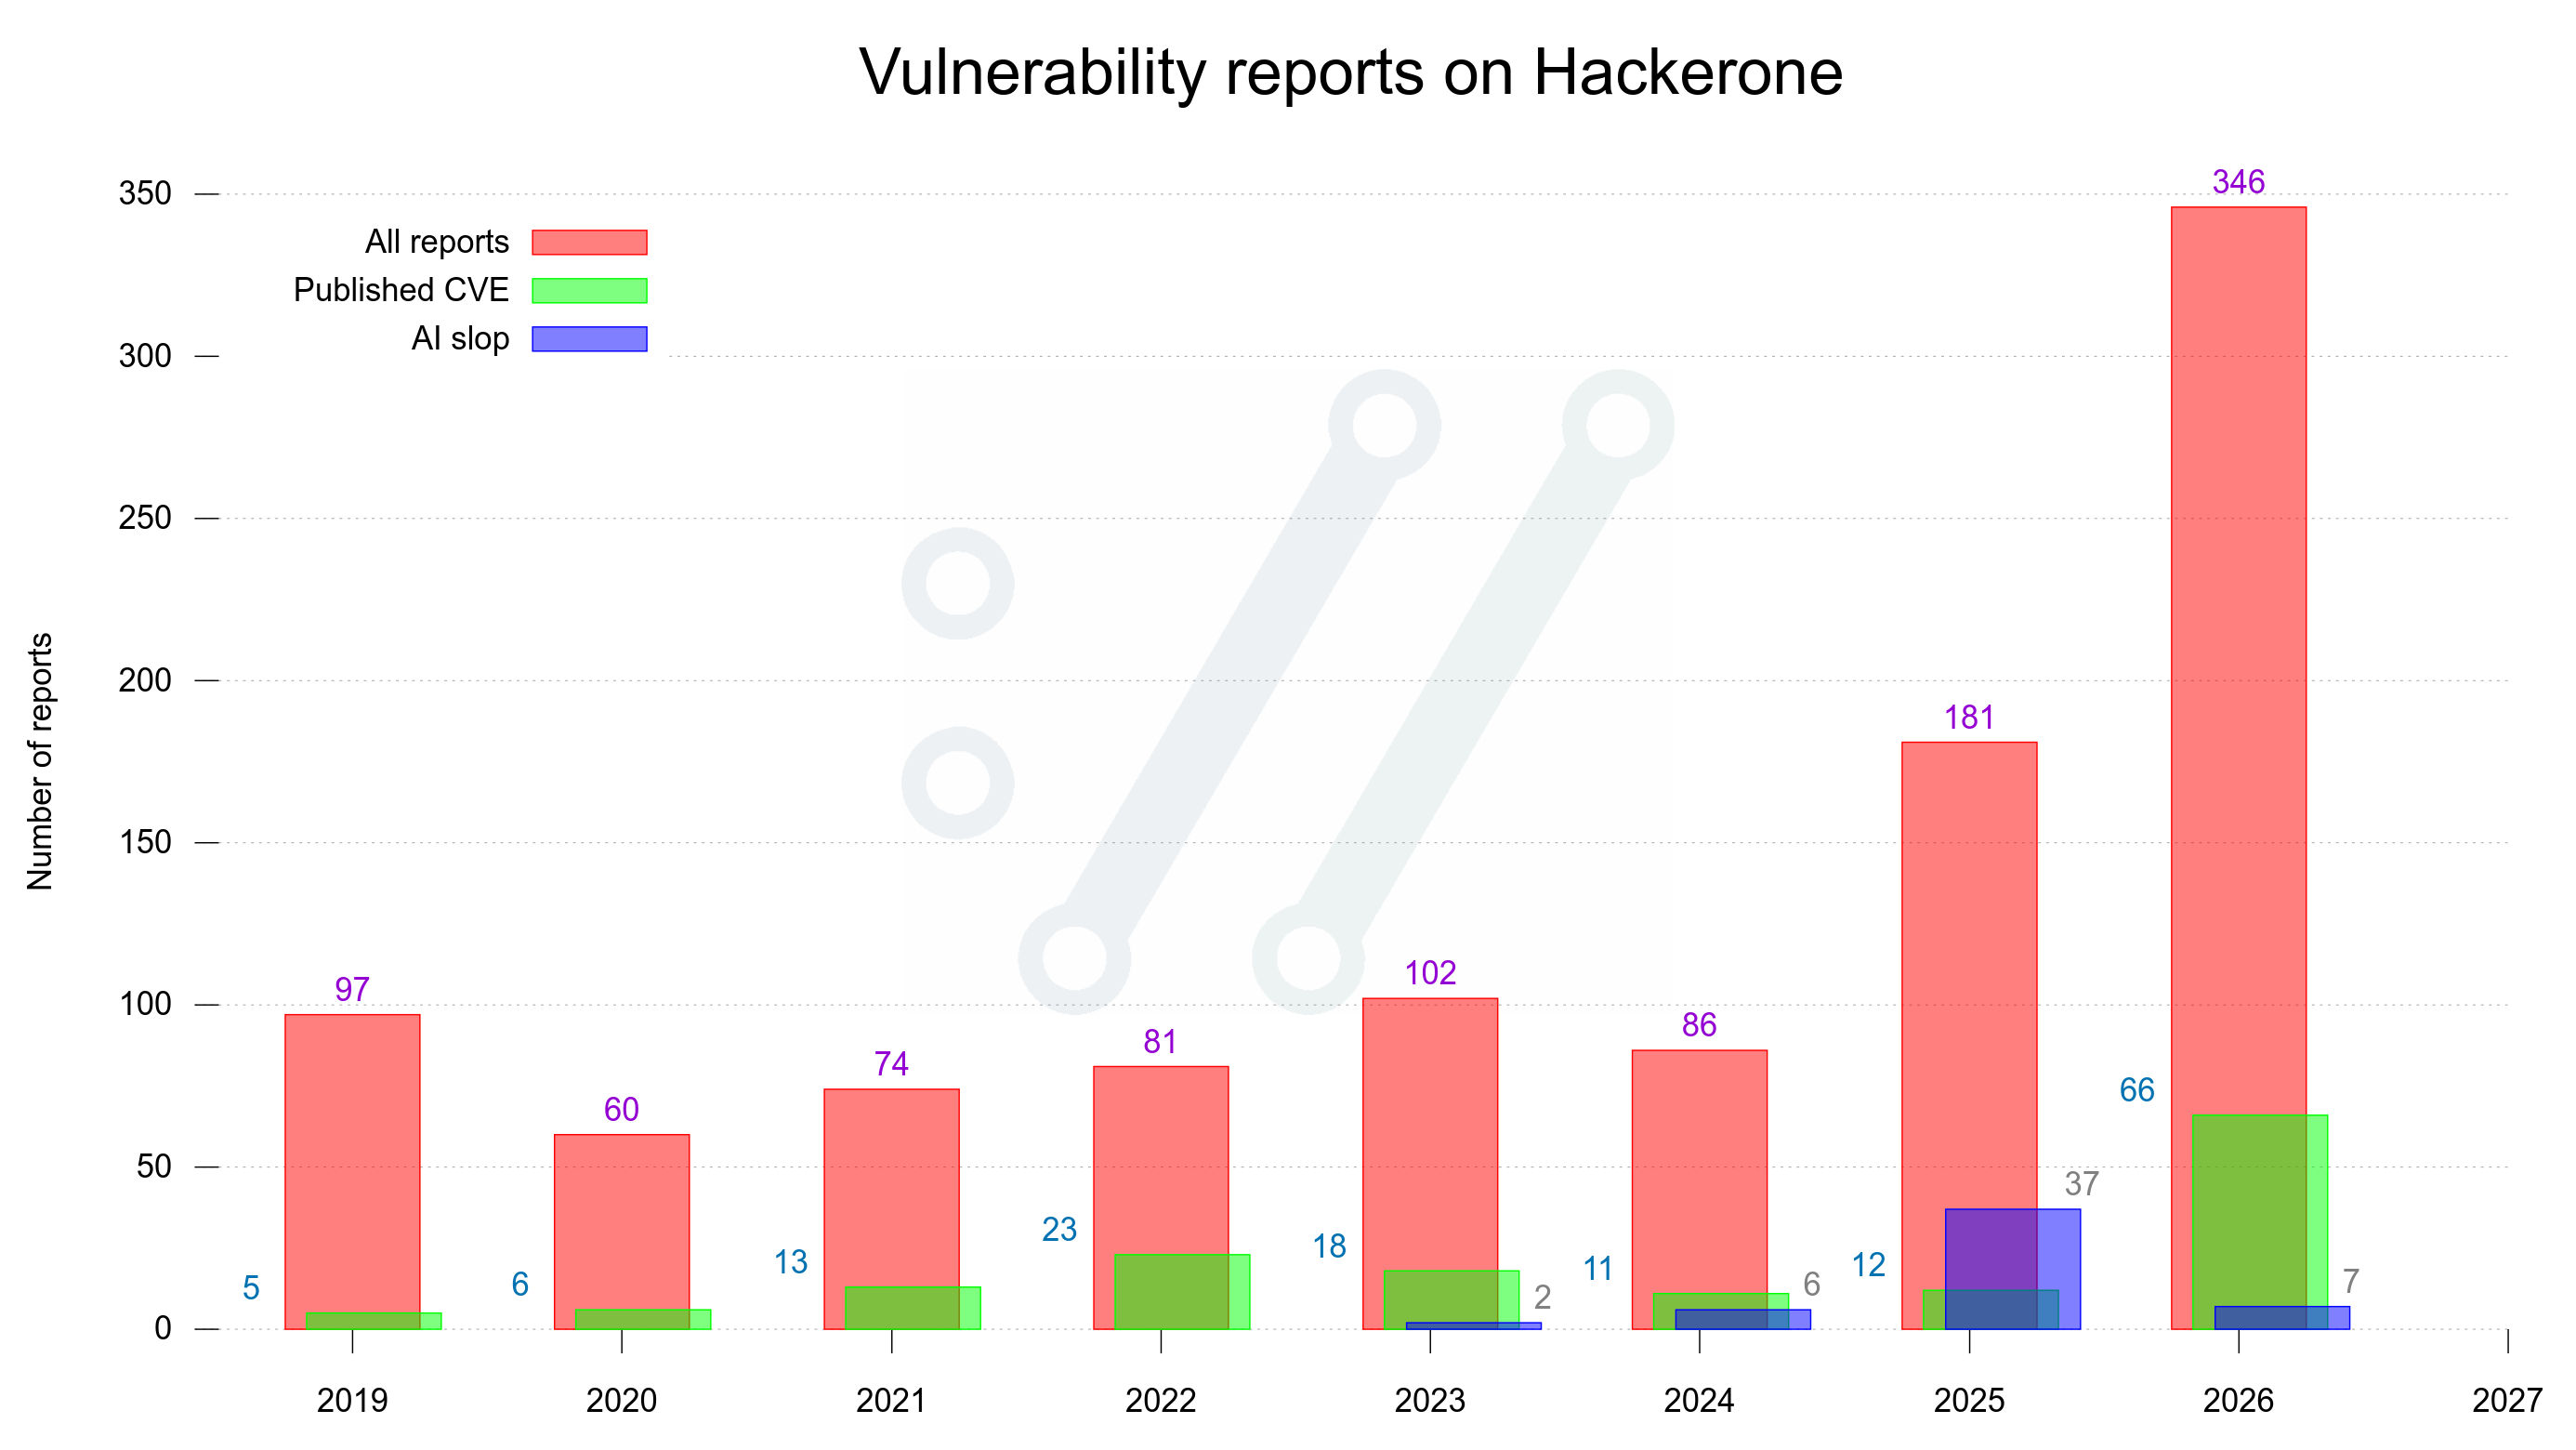
We started the hackerone program in April 2019. We have received 1,030 vulnerability reports over these 7.5 years.

More than a third of the reports were submitted in 2026.

@bagder@mastodon.social

Do minor vulnerabilities in the open

(Starting Monday October 26)

daniel.haxx.se/blog/2026/10/20

@bagder@mastodon.social

At our maintainer meeting tonight we decided to move forward with the "handle LOW/MED vuln reports openly on GitHub".

Now we just need to get the documentation and processes adjusted, then push the button to do this. Maybe write a blog post too. So, ideally within this week.

Stay tuned

@bagder@mastodon.social

At 32 vulnerability submissions since Saturday morning.

All of them are MUCH too long without explaining the problem up front in a few human written sentences. Most of them identify a problem. Many of them overstate the problem. Many of them claim a vulnerability when its just a minor bug.

@bagder@mastodon.social

Four years ago, the project was part of the Sovereign Tech Fund's pilot program and we improved a bit: daniel.haxx.se/blog/2022/10/19

@icing@chaos.social

In reply to @icing@chaos.social

In computer science, this would be regarded as s flow control problem. The solution: limit your inbox window, drop incoming data beyond that.

This did during its Summer of Bliss 2026.

BUT: this is not allowed in the CVE system.

So, everyone look away while we did this, requiring us to immediately start working should something really bad prop up. Or else.

@icing@chaos.social

The simple observation:

The project is getting DoS‘ed by security researchers.

No mal intent, but driven by stock/work market evaluations.

Example: Aisle has shown its value by the curl CVEs claimed and was now bought by Cohere, presumably a good deal for both companies.

Economically reasonable behaviour for both. The FOSS projects are the roadkill, though.

All reporters have similar motivations, down to individuals improving their personal market value.

@bagder@mastodon.social

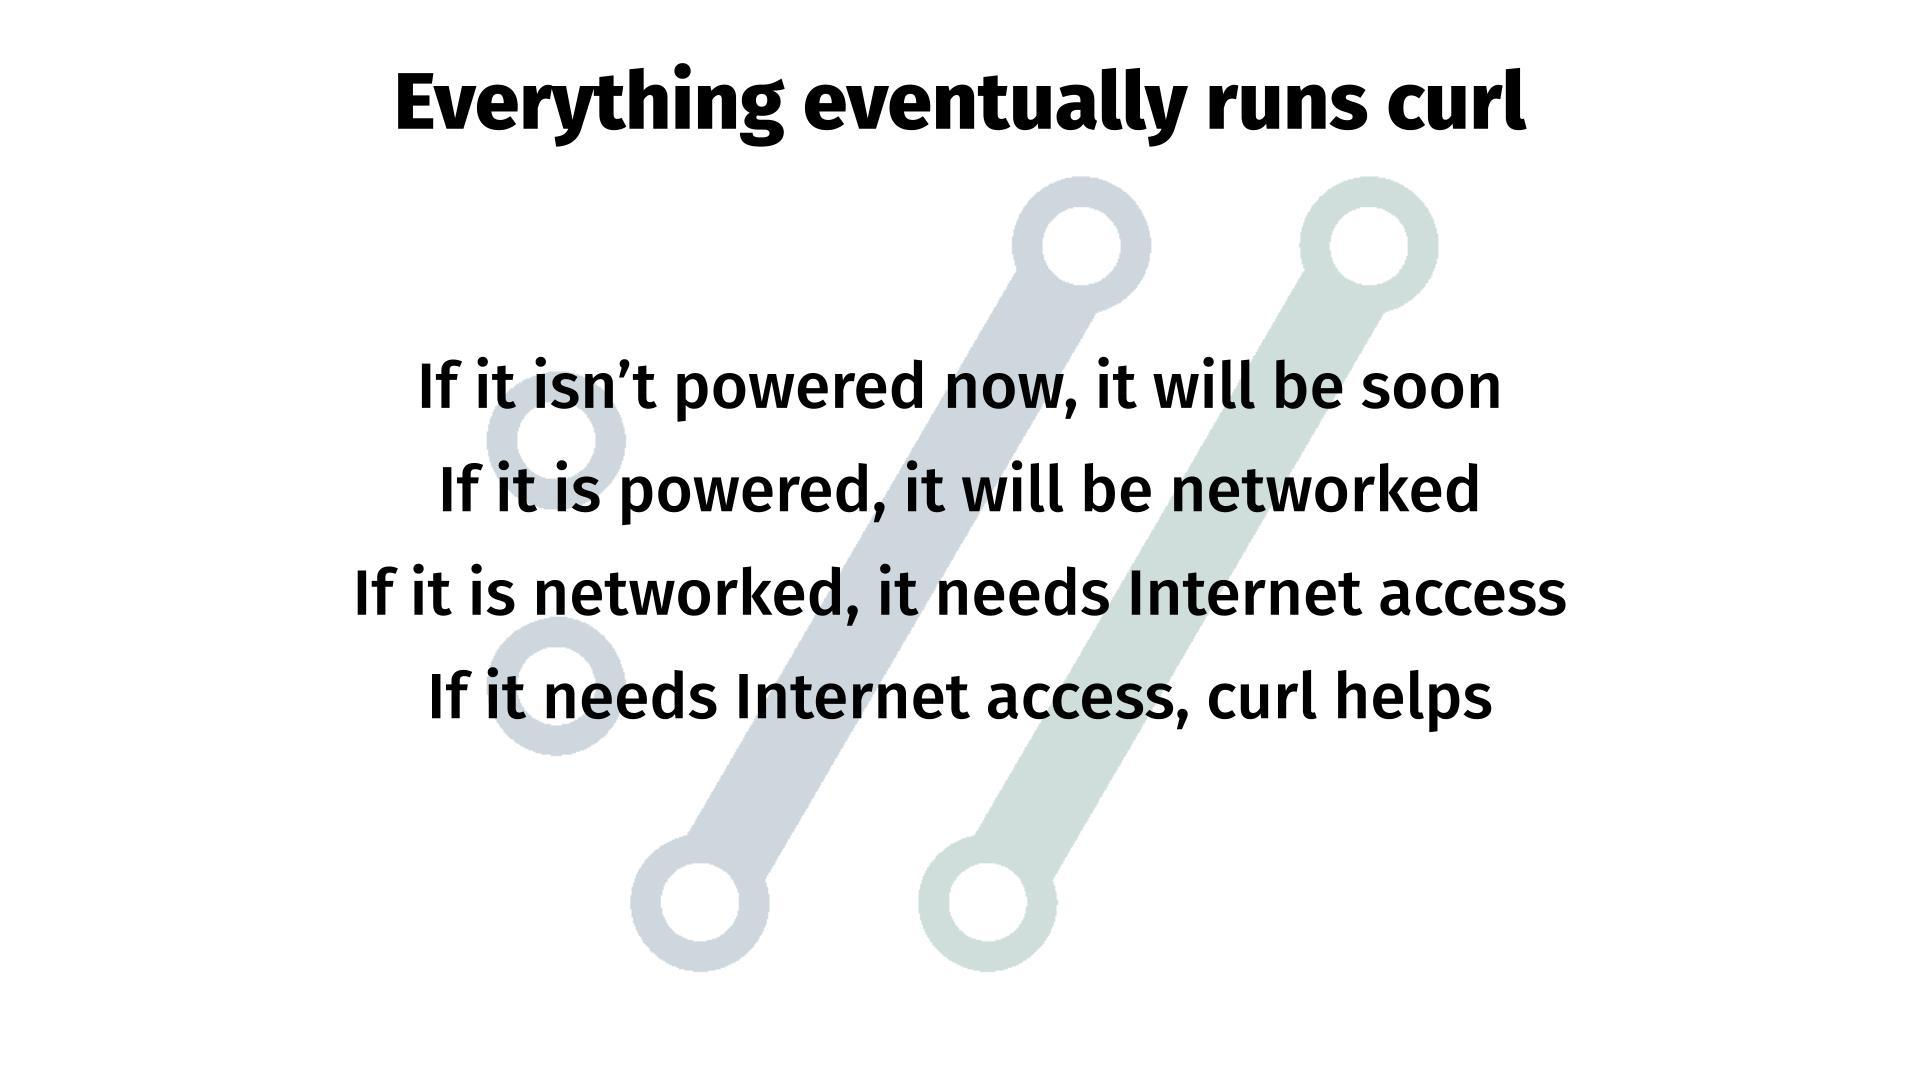
's law: Everything eventually runs curl

A trend in society over the last decade and I don't see it changing anytime soon.

If it isn’t powered now, it will be soon
If it is powered, it will be networked
If it is networked, it needs Internet access
If it needs Internet access, curl helps
@bagder@mastodon.social

Hello .

We are deeply disappointed that you have started to require ID verification from hackers who want to submit vulnerability reports to , as this now makes them turn away and we miss out on their reports.

We have not been a bug bounty program since February and we do not intend to go back to bounties. What do we need to do for you to switch us to "just" a Vulnerability Disclosure Program so that you can stop requiring ID from security researchers trying to help us out?

@bagder@mastodon.social

Just 36 hours after the previous release, we are already at three pending CVE announcements queued up... 😰